IBM Acquires Logiq Consulting to Expand UK Sovereign Defence, CNI, and NCSC-Assured Cybersecurity
By Vatsal Shah | September 24, 2026 | 8 min read | Source: IBM Newsroom
- Sovereign Cyber Expansion: On September 24, 2026, IBM announced the acquisition of Logiq Consulting, an elite, NCSC-assured (National Cyber Security Centre) cybersecurity consultancy based in the United Kingdom.
- Mission Critical Focus: Logiq specializes in architecting high-assurance security architectures, cyber risk assurance, and compliance frameworks for UK Defence, Critical National Infrastructure (CNI), and high-integrity public sector agencies.
- Synergy with SiXworks: The acquisition enhances IBM Consulting by pairing Logiq’s sovereign cyber assurance expertise with SiXworks (an IBM company established in UK defence engineering), forming an integrated end-to-end mission transformation powerhouse.
- Sovereign AI & Hybrid Cloud Anchor: IBM ties this strategic buy directly to digital sovereignty—enabling UK defense and public sector organizations to adopt hybrid cloud and AI capabilities while preserving total custody, cryptographic boundaries, and compliance with the NCSC Cyber Assessment Framework (CAF).
- Transaction Terms: Financial details and purchase price were not disclosed in the official release, maintaining standard IBM corporate M&A disclosure protocol for specialized consultancy tuck-ins.
Lead Paragraph
LONDON, United Kingdom — On September 24, 2026, IBM announced that it has acquired Logiq Consulting, a prominent United Kingdom cybersecurity consultancy recognized as an NCSC-assured provider by the National Cyber Security Centre. Published via the IBM Newsroom, the transaction sharply accelerates IBM Consulting's capacity to deliver sovereign cybersecurity, classified architecture advisory, and secure digital transformation across the UK Ministry of Defence (MoD), national security apparatus, Critical National Infrastructure (CNI), and highly regulated public bodies. By integrating Logiq's certified security architects alongside SiXworks—an IBM company dedicated to defence mission software and systems engineering—IBM creates a unified, security-cleared consulting practice designed to guide regulated institutions through hybrid cloud modernizations and sovereign artificial intelligence deployments. In accordance with IBM's standard policy for private consultancy acquisitions, financial terms and transaction multiples were not disclosed.
What Happened: Strategic Acquisition Overview
The modern global threat landscape has placed national infrastructure, sovereign supply chains, and defence establishments under unrelenting hybrid pressure. From advanced persistent threats (APTs) targeting energy grids and naval logistics to the complex compliance mandates governing classified cloud migration, sovereign clients in the UK face an acute deficit of security-cleared, accredited cybersecurity architects.
Logiq Consulting established an enviable reputation in the UK market by bridging the gap between high-level national security directives and tangible systems implementation. As an NCSC Assured Cyber Security Consultancy, Logiq’s personnel possess the verified qualifications, clearances, and institutional pedigree necessary to audit, design, and certify critical systems handling secret and above information assets.
┌─────────────────────────────────────────────────────────────────────────────┐
│                   IBM / LOGIQ CONSULTING TRANSACTION PROFILE                │
├───────────────────────────┬─────────────────────────────────────────────────┤
│ Transaction Parameter     │ Verified Specification                          │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Acquirer                  │ International Business Machines Corporation (IBM│
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Target Firm               │ Logiq Consulting Ltd (Bristol / UK)             │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Announcement Date         │ September 24, 2026                              │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Transaction Type          │ Capability & Talent Acquisition (Tuck-in)       │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Core Assurance Accredit   │ NCSC Assured Cyber Security Consultancy (GCHQ)  │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Key Sector Domains        │ UK Defence · Intelligence · CNI · Central Gov   │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Sister Unit Integration   │ SiXworks (an IBM Company, Defence Engineering)  │
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Strategic Tech Imperative │ Digital Sovereignty · Hybrid Cloud · Sovereign AI│
├───────────────────────────┼─────────────────────────────────────────────────┤
│ Financial Consideration   │ Undisclosed (Not Provided in Release)           │
└───────────────────────────┴─────────────────────────────────────────────────┘
By bringing Logiq into IBM Consulting, IBM addresses the paramount bottleneck facing large-scale public sector digital transformations: the requirement that transformation partners possess sovereign operational pedigree, domestic clearance infrastructure, and verified compliance with UK defense security standards (such as DefStan 05-138 and the NCSC Cyber Assessment Framework).
Architectural Deep Dive: UK Sovereign Defence & CNI Cybersecurity
To understand why this acquisition represents a structural leap for IBM in the UK, one must examine the multi-tiered architecture required to deliver digital transformation within regulated government and critical infrastructure boundaries.
Modern sovereign programs cannot simply deploy commercial public cloud architectures or unverified offshore development teams. They require a zero-trust, multi-layered sovereign operational stack:
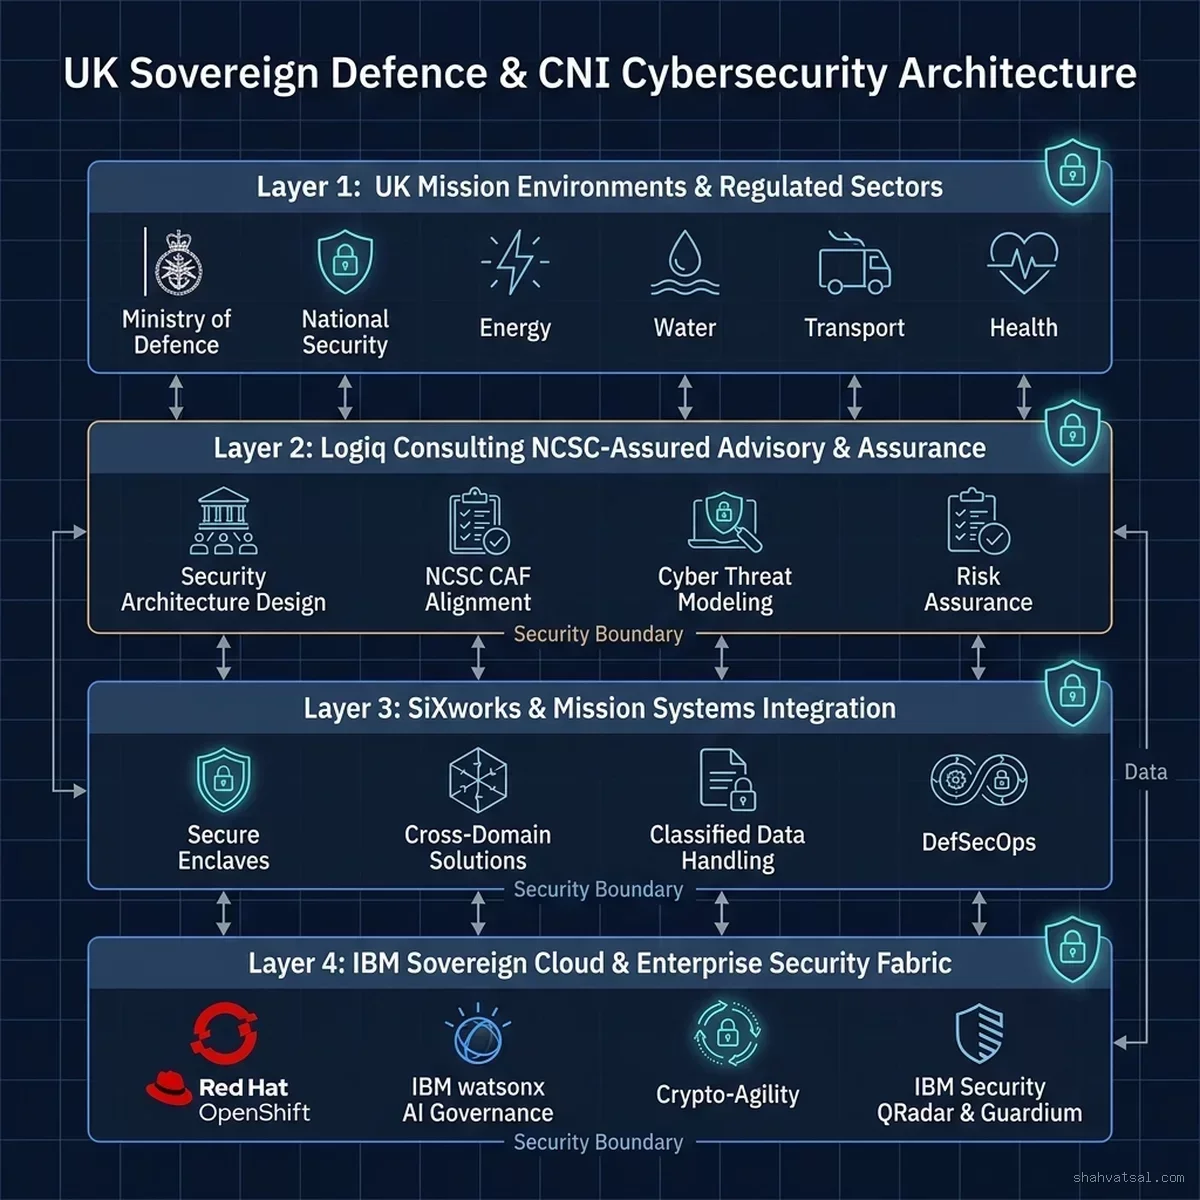
As illustrated in the system architecture model above, the integration of Logiq Consulting completes a four-layer sovereign capability stack:
Layer 1: UK Mission Environments & Regulated Sectors
At the pinnacle sit the demanding mission environments:
- Ministry of Defence (MoD): Joint Forces Command, Defence Digital, land, air, and maritime operational networks requiring strict compartmentalization.
- National Security & Intelligence: Intelligence hubs requiring high-integrity cryptographic boundaries.
- Critical National Infrastructure (CNI): Civil nuclear installations, the national electrical transmission grid, water utilities, transport routing, and public healthcare backbones.
Layer 2: Logiq Consulting NCSC-Assured Advisory & Assurance
This newly acquired layer provides the indispensable trust and accreditation bridge:
- Security Architecture Design: Authoring high-assurance, defensible architectures from scratch, mapping every interface against NCSC design principles.
- NCSC CAF Alignment: Conducting comprehensive Cyber Assessment Framework audits to benchmark operational resilience against nation-state threat vectors.
- Cyber Threat Modeling & Attack Surface Discovery: Proactively modeling supply chain vulnerabilities and advanced adversary vectors before systems enter production.
- Accreditation & Risk Assurance: Preparing sovereign risk dossiers (SAC and DefStan documentation) required for senior information risk owners (SIROs) to grant operational authorization.
Layer 3: SiXworks & Mission Systems Integration
Complementing Logiq is SiXworks, an IBM company acquired to deliver agile, security-cleared digital engineering:
- Secure Enclaves: Building air-gapped, sovereign cloud environments capable of running complex data workloads under classified operational parameters.
- Cross-Domain Solutions (CDS): Engineering certified data diodes and filter guards that allow data to flow safely between different security classification boundaries without risking spillover.
- Classified Data Handling & DefSecOps: Implementing automated, secure software delivery pipelines that adhere strictly to UK Ministry of Defence security principles.
Layer 4: IBM Sovereign Cloud & Enterprise Security Fabric
At the foundation, IBM provides the enterprise technology stack that powers large-scale sovereign modernization:
- Red Hat OpenShift Sovereign Fabrics: Delivering containerized, air-gappable infrastructure that runs identically on sovereign bare metal, secure private clouds, or approved commercial sovereign partitions.
- IBM watsonx AI Governance: Enforcing automated model validation, data lineage tracking, and policy enforcement to prevent proprietary defense data from leaking into public foundational models.
- Crypto-Agility & Post-Quantum Encryption: Engineering systems that can dynamically swap cryptographic ciphers as NIST and NCSC post-quantum cryptography standards mature.
- IBM Security QRadar & Guardium: Providing enterprise-scale security information event management (SIEM), extended detection and response (XDR), and sensitive data activity monitoring.
The Regulated Environments Cybersecurity & AI Governance Lifecycle
A defining challenge in modern defense and CNI procurement is that security cannot be treated as an afterthought or a final compliance checklist. Sovereign environments demand a closed-loop governance lifecycle where threat assessment, architectural isolation, AI telemetry, and continuous assurance operate synchronously.
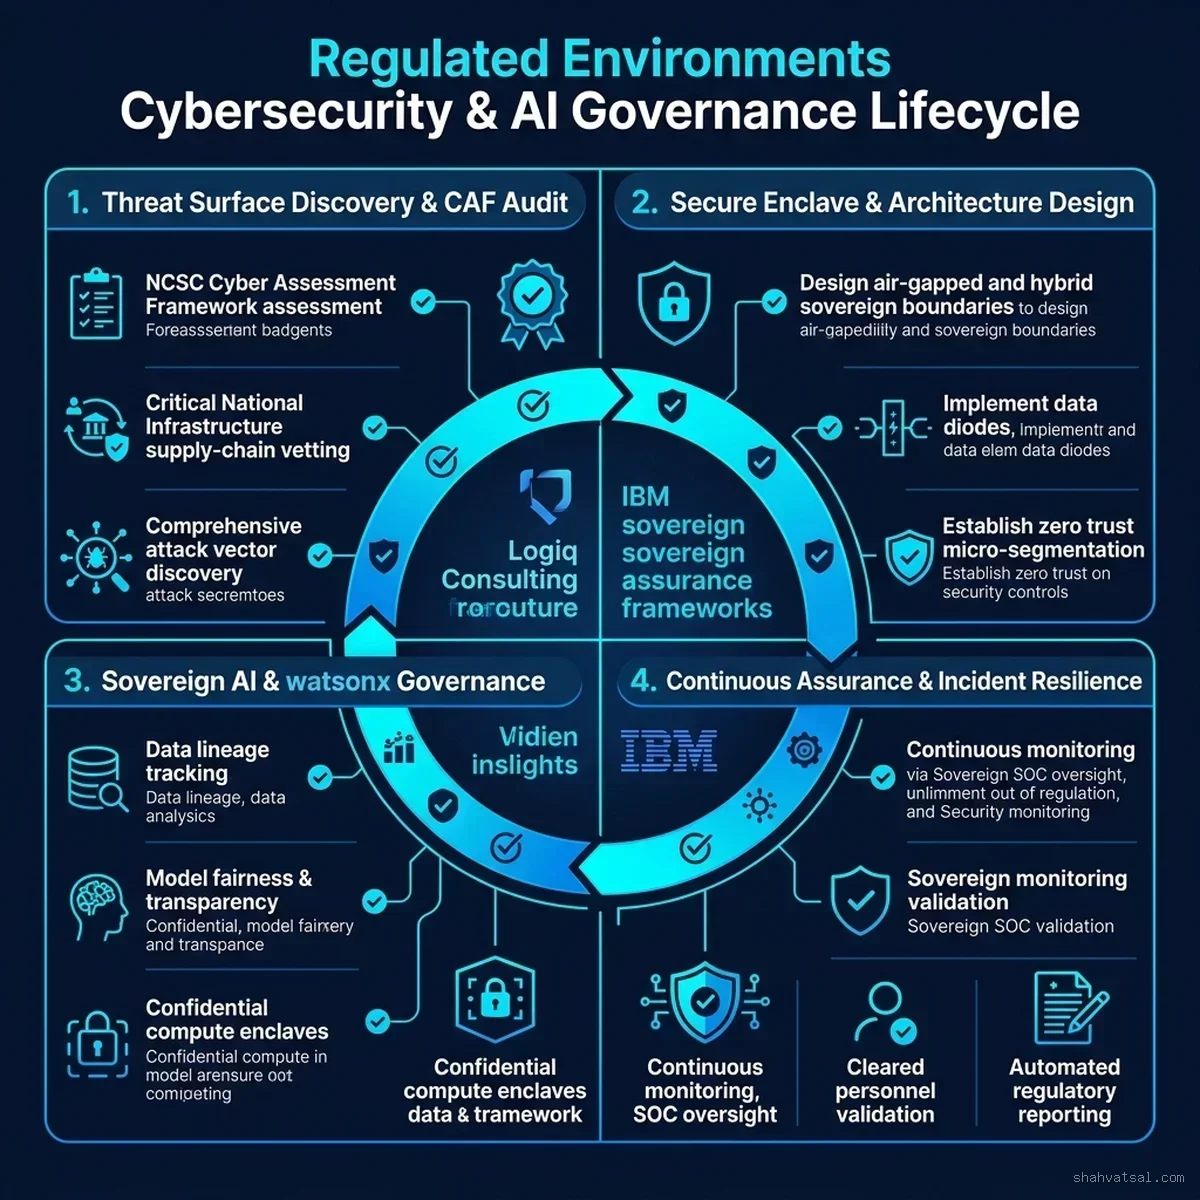
As depicted in the governance lifecycle matrix above, the combined IBM and Logiq capability operates across four cyclical quadrants:
1. Threat Surface Discovery & CAF Audit
The lifecycle commences with rigorous, adversarial discovery. Using NCSC Cyber Assessment Framework methodologies, Logiq's certified consultants dissect the client’s legacy ecosystem, assessing physical, logical, and supply-chain vulnerabilities. Unlike automated commercial vulnerability scans, this process models nation-state threat capabilities, third-party component vulnerabilities, and human credential exposure across critical command paths.
2. Secure Enclave & Architecture Design
Once risk profiles are quantified, architects design mathematically verifiable security boundaries. This includes deploying unidirectional data diodes, micro-segmented zero trust software-defined perimeters, and hardware security modules (HSMs). Architecture blueprints are generated to ensure that data at rest, data in transit, and data in execution remain cryptographically isolated within accredited national boundaries.
3. Sovereign AI & watsonx Governance
As defense and infrastructure operators deploy generative AI and machine learning for predictive maintenance, battlefield intelligence, and operational routing, sovereignty becomes paramount. IBM watsonx provides automated metadata tagging, lineage tracking, and bias detection, ensuring that algorithmic models deployed in classified enclaves remain explainable, unpoisoned, and completely under sovereign jurisdictional custody.
4. Continuous Assurance & Incident Resilience
The lifecycle culminates in active resilience. Sovereign Security Operations Centers (SOCs) staffed by vetted personnel monitor real-time telemetry, correlating anomalies via IBM Security platforms. Compliance reports are programmatically generated for regulatory oversight bodies, while red team exercises continually challenge operational defenses to validate incident response playbooks.
Strategic Capabilities Comparison: Standalone vs Integrated Enterprise Platform
To evaluate the commercial and operational impact of this acquisition, it is instructive to compare how cybersecurity advisory was delivered historically versus the unified platform model IBM now offers:
| Operational Dimension | Standalone Boutique Cyber Consultancies | Large General-Purpose IT Integrators | IBM + Logiq Consulting + SiXworks Combined Platform |
|---|---|---|---|
| NCSC Assurance Status | Often NCSC-assured, but lack systems integration scale | Rare NCSC accreditation; relies on subcontractors | Direct NCSC-assured accreditation paired with global delivery scale |
| UK Defence Clearance Density | High percentage of SC/DV cleared personnel, limited bench size | Low clearance density; struggles with classified enclaves | Comprehensive bench of UK SC and DV cleared architects and engineers |
| End-to-End Delivery | Limited to advisory reports, audits, and documentation | Delivers integration, but struggles with sovereign security compliance | Full lifecycle: Advisory → Architecture → Software Delivery → Managed Cloud |
| Hybrid Cloud Infrastructure | Cloud-agnostic recommendations, no proprietary infrastructure platform | Vendor-locked public hyperscaler implementations | Red Hat OpenShift sovereign hybrid cloud across air-gapped and hybrid clouds |
| Sovereign AI Governance | Theoretical policy documents with little tooling enforcement | Commercial cloud APIs that may violate data sovereignty mandates | Enterprise watsonx governance enforcing data residency and model auditability |
| Post-Quantum Preparedness | High-level risk alerts without remediation tooling | Early stage, depends on third-party security software vendors | Proprietary IBM crypto-agile libraries and quantum-resistant security toolsets |
This comparison underscores why sovereign clients prefer integrated partners. In high-consequence environments, the handoff between a boutique advisory firm that writes a security recommendation and a large systems integrator that attempts to build it is historically where security vulnerabilities, cost overruns, and accreditation failures occur.
Dedup & Geopolitical Context: The Sovereign Cyber Consolidation Wave
The acquisition of Logiq Consulting by IBM does not occur in a vacuum. It is part of a deliberate wave of sovereign defense and intelligence consolidation sweeping Western technology providers in 2026. However, it is essential to distinguish this acquisition from adjacent industry developments:
1. Distinction from Airbus / Quarkslab (#N143)
On October 1, 2026, Airbus Defence and Space finalized the acquisition of French cybersecurity specialist Quarkslab (backed by Tikehau Capital). While both deals involve European defense and security, their technological mechanics are fundamentally distinct:
- Airbus / Quarkslab: A product-centric software acquisition focused on Quarkslab’s QShield technology, which prevents AI models, mobile applications, and embedded aerospace firmware from being reverse-engineered or tamper-exploited by hostile adversaries.
- IBM / Logiq Consulting: A specialized sovereign consultancy and advisory acquisition focused on UK NCSC-assured security architecture, CAF risk assurance, and public sector mission transformation.
2. Distinction from SAIC / ISC (#N142)
On October 5, 2026, SAIC completed its acquisition of ISC (Innovative Solutions Consortium):
- SAIC / ISC: Focused on US Department of Defense and federal intelligence agency zero-trust identity architectures and post-quantum cryptographic transitions under US federal mandates (NIST and CISA guidelines).
- IBM / Logiq Consulting: Tailored specifically to the sovereign jurisdiction of the United Kingdom, answering directly to Cabinet Office and NCSC governance frameworks.
3. Distinction from Commercial Hyperscaler Gov Clouds (#N82)
While platforms like Anthropic’s Claude for Government (#N82) or AWS Secret Region provide hosted commercial infrastructure, the IBM-Logiq-SiXworks model addresses the bespoke architectural design and regulatory certification required before any sovereign cloud workload can be authorized for operation.
Legal Disclaimers & Regulatory Notices
To ensure complete legal rigor, compliance transparency, and intellectual property accuracy, the following parameters are formally noted:
┌─────────────────────────────────────────────────────────────────────────────┐
│                       LEGAL & INTELLECTUAL PROPERTY NOTICE                  │
├─────────────────────────────────────────────────────────────────────────────┤
│ 1. Trademark Ownership: IBM and the IBM 8-bar logo are registered trademarks │
│    of International Business Machines Corporation in the United States and  │
│    other countries. Red Hat, OpenShift, watsonx, QRadar, and Guardium are    │
│    trademarks or registered trademarks of IBM and its subsidiaries.         │
│ 2. Third-Party Trademarks: Logiq Consulting is a registered trademark of    │
│    Logiq Consulting Ltd. National Cyber Security Centre (NCSC) and GCHQ are │
│    Crown Copyright and official marks of the United Kingdom Government.     │
│ 3. Transaction Disclosures: Financial terms, deal valuation, and employee   │
│    headcount metrics were not disclosed in the official IBM announcement of │
│    September 24, 2026. All operational assertions reflect official corporate│
│    announcements and public regulatory accreditation registries.            │
│ 4. Editorial Independence: This publication constitutes independent technical│
│    analysis and architectural review. No sponsorship or endorsement is      │
│    expressed or implied by IBM, Logiq Consulting, or UK Crown entities.    │
└─────────────────────────────────────────────────────────────────────────────┘
Strategic Implications for UK Defence & CNI Leaders
For Chief Information Security Officers (CISOs), Chief Information Officers (CIOs), and digital transformation directors across UK Defence, national security, and critical national infrastructure, the acquisition of Logiq Consulting by IBM offers several immediate takeaways:
- Accelerated Pathway to NCSC CAF Accreditation: Organizations struggling to achieve compliance with the National Cyber Security Centre's Cyber Assessment Framework can now engage IBM for both architectural assessment and end-to-end technical implementation under a single contractual framework.
- De-risking Cloud and AI Deployments: As pressure mounts on government departments to adopt AI-driven automation, the combined IBM-Logiq practice provides the clearance-vetted personnel required to ensure that model training, data ingestion, and inference pipelines do not compromise sovereign data boundaries.
- Closing the Engineering-Assurance Gap: By pairing Logiq's advisory assurance with SiXworks' hands-on defense software engineering, defense clients avoid the friction of translating abstract security policies into deployed Kubernetes and OpenShift infrastructure.
- Resilience Against Nation-State Supply Chain Attacks: With increasing regulatory scrutiny placed on third-party software supply chains, Logiq's threat modeling methodologies provide critical infrastructure operators with auditable proof of software component integrity.
As sovereign states worldwide fortify their digital perimeters, IBM's acquisition of Logiq Consulting demonstrates that the future of enterprise IT consulting will not be won by generalist scale alone, but by the ability to deliver verified, sovereign trust in the world's most demanding operational environments.
Frequently Asked Questions
What did IBM announce regarding Logiq Consulting?
On September 24, 2026, IBM announced the acquisition of Logiq Consulting, an award-winning UK cybersecurity consultancy assured by the National Cyber Security Centre (NCSC). The acquisition significantly expands IBM Consulting's secure digital transformation and cyber advisory footprint across UK Defence, Critical National Infrastructure (CNI), and the wider public sector.
Were the financial terms or purchase price of the Logiq Consulting acquisition disclosed?
No. IBM did not disclose the financial details, valuation, or purchase price for the acquisition of Logiq Consulting in its official newsroom announcement.
What is an NCSC-assured cybersecurity consultancy?
An NCSC-assured consultancy has undergone rigorous technical auditing by the UK National Cyber Security Centre (part of GCHQ) to certify that its practitioners, methodologies, security architecture standards, and risk advisory frameworks meet the stringent operational requirements demanded by UK government departments, intelligence bodies, and sovereign defence programs.
How does Logiq Consulting fit alongside IBM's previous acquisition of SiXworks?
Logiq Consulting operates synergistically alongside SiXworks, an IBM company acquired to deliver mission-critical digital systems and software engineering for UK defence and security clients. While SiXworks provides hands-on digital mission engineering and agile delivery, Logiq contributes specialized cyber architecture, threat modeling, and NCSC-certified risk assurance.
How does this acquisition relate to digital sovereignty and sovereign AI?
IBM specifically linked the acquisition to helping UK clients navigate hybrid cloud and artificial intelligence adoption while maintaining complete sovereign data control, cryptographic security, and regulatory compliance under the UK Cyber Assessment Framework (CAF) and sovereign defence mandates.